


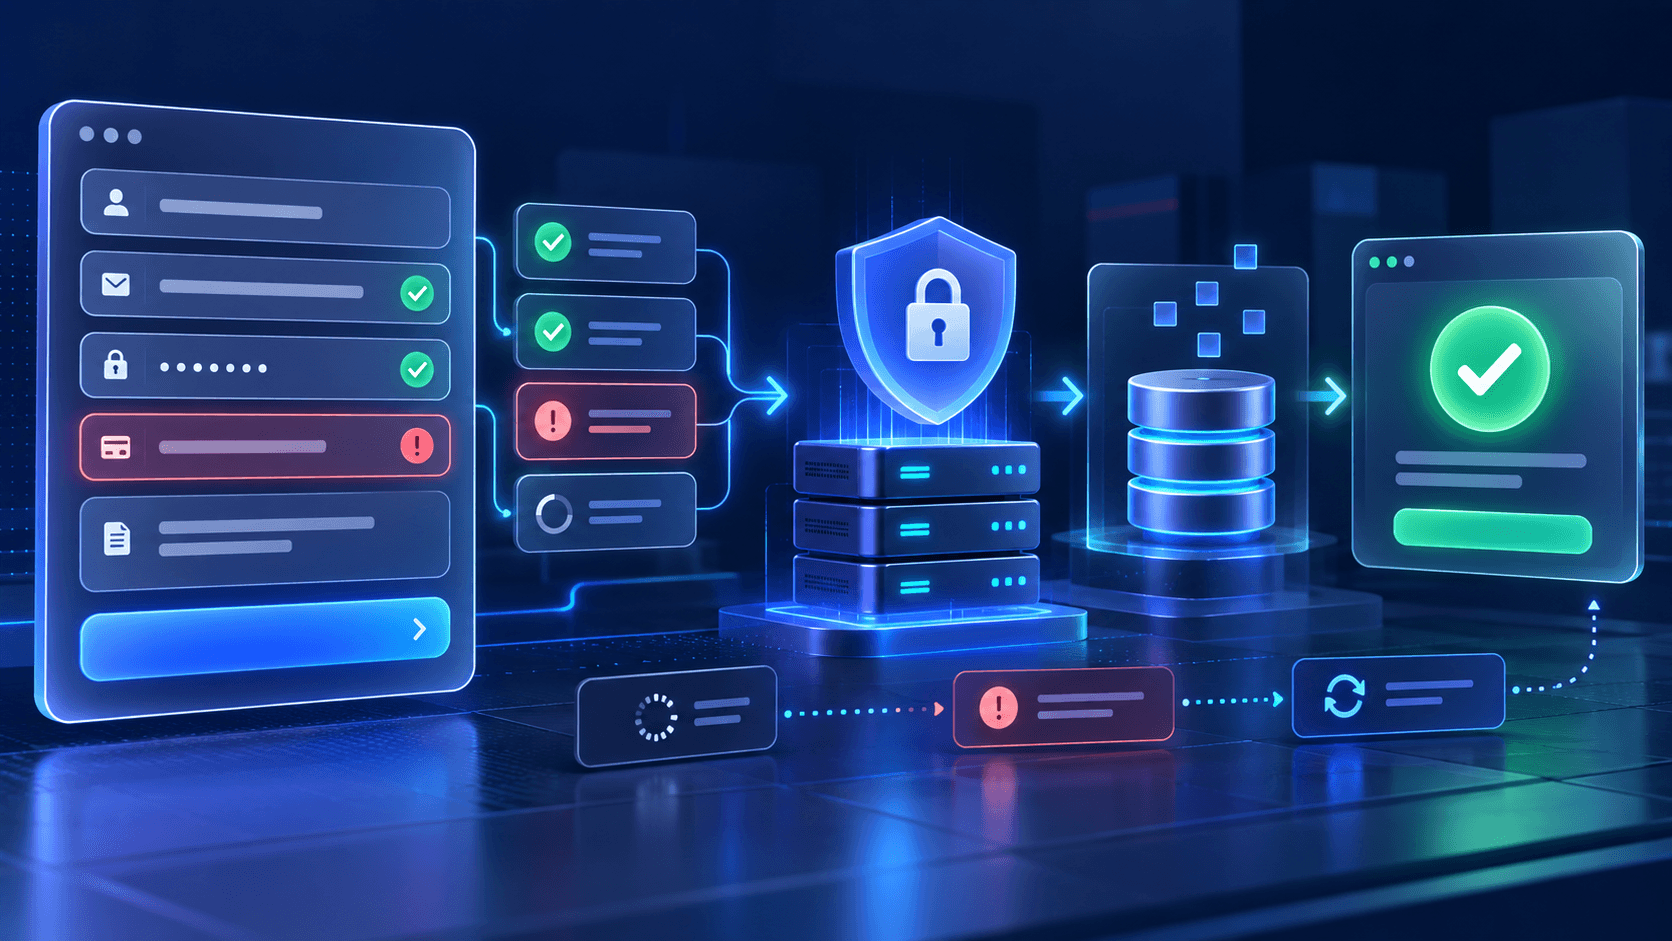
Define the form as a user-visible contract
A form is not merely a collection of inputs. It is a workflow with an entry state, validation rules, a submission boundary, a success outcome, and recovery paths. Before choosing a library, write down what the user is trying to complete and which fields are truly necessary.
Input contract
Names, formats, limits, dependencies, optional fields, and accepted files.
Submission contract
Identity, authorization, duplicate behavior, deadlines, and safe retries.
Outcome contract
Field feedback, global errors, confirmation, navigation, and recovery.
Keep the server contract independent from the current interface so a mobile client, API integration, or redesigned form follows the same business rules.
Use client validation for guidance and server validation for trust
Browser validation should help users correct mistakes without waiting for a request. It cannot protect the application because requests can bypass the interface. Parse and validate every submitted value on the server before database writes or provider calls.
const result = contactSchema.safeParse(req.body);

if (!result.success) {
  return res.status(400).json({
    ok: false,
    fields: toFieldErrors(result.error),
  });
}

const contact = await createContact(result.data);
Normalize deliberately, reject unknown fields where appropriate, set maximum lengths and collection sizes, and validate relationships such as an end date occurring after a start date.
Make errors understandable without relying on color
Give every control a persistent label, associate help and error text with the field, and keep instructions visible when they remain relevant. On failed submission, move focus to a concise error summary that links to invalid controls while preserving every valid value.
- Use native controls and semantic groups before custom widgets.
- Announce asynchronous status changes through an appropriate live region.
- Show errors in text and avoid color-only meaning.
- Keep keyboard focus visible and test the complete flow without a mouse.
- Use autocomplete tokens for common identity, address, and payment fields.
Test accessibility in the same automated and browser layers described in our React accessibility testing guide.
Model idle, submitting, success, and failure explicitly
Disable repeated intent while a request is actively submitting, but do not make the entire page inert. Keep a visible progress label, preserve the user's input on recoverable failure, and provide a retry only when repeating the request is safe.
After success, show what happened and what comes next. If navigation follows, ensure the destination contains a durable confirmation rather than depending on a transient toast.
Authorize the mutation beside the data it changes
Read trusted identity on the server and authorize it against the specific record, tenant, or capability. Hidden inputs, disabled fields, route parameters, and client state remain attacker-controlled. Apply rate limits to costly or abuse-prone actions and never return stack traces, tokens, or private record details.
Protect file inputs with type, size, and content checks, store uploads outside executable paths, and scan where the risk model requires it. For Server Actions, use the boundary checklist in our Next.js Server Actions security guide.
Protect drafts from long forms and unreliable networks
For long or consequential workflows, save deliberate drafts, communicate the saved state, and define what happens when the same record changes elsewhere. Do not persist passwords, payment data, or secrets in browser storage. Expire server drafts and make ownership checks part of every load and update.
Set request deadlines, distinguish validation failures from temporary dependency failures, and retain an opaque request ID in the user-facing error. The conflict and recovery patterns in our React autosave guide help with multi-step and draft-heavy experiences.
Measure completion quality, not only submissions
Track form starts, field error frequency, abandonment, submission latency, duplicate attempts, successful completion, and downstream business outcomes. Segment by device and route while avoiding sensitive field values in logs or analytics.
High validation failure on one field may reveal confusing copy or the wrong input model. A successful HTTP response is not enough if the record fails to reach the CRM, payment provider, or follow-up workflow.
Next.js production forms checklist
✓ Every field supports the user's task
✓ Server validation owns the trust boundary
✓ Labels and errors are programmatically associated
✓ Submission states are explicit and visible
✓ Important mutations prevent duplicates durably
✓ Authorization checks the specific resource
✓ Long workflows have safe draft recovery
✓ Analytics exclude sensitive values
Build a more dependable Next.js application
Endurance Softwares helps teams design, build, test, and operate production-ready Next.js platforms.