


Use a BFF to serve a client experience, not to rename the backend
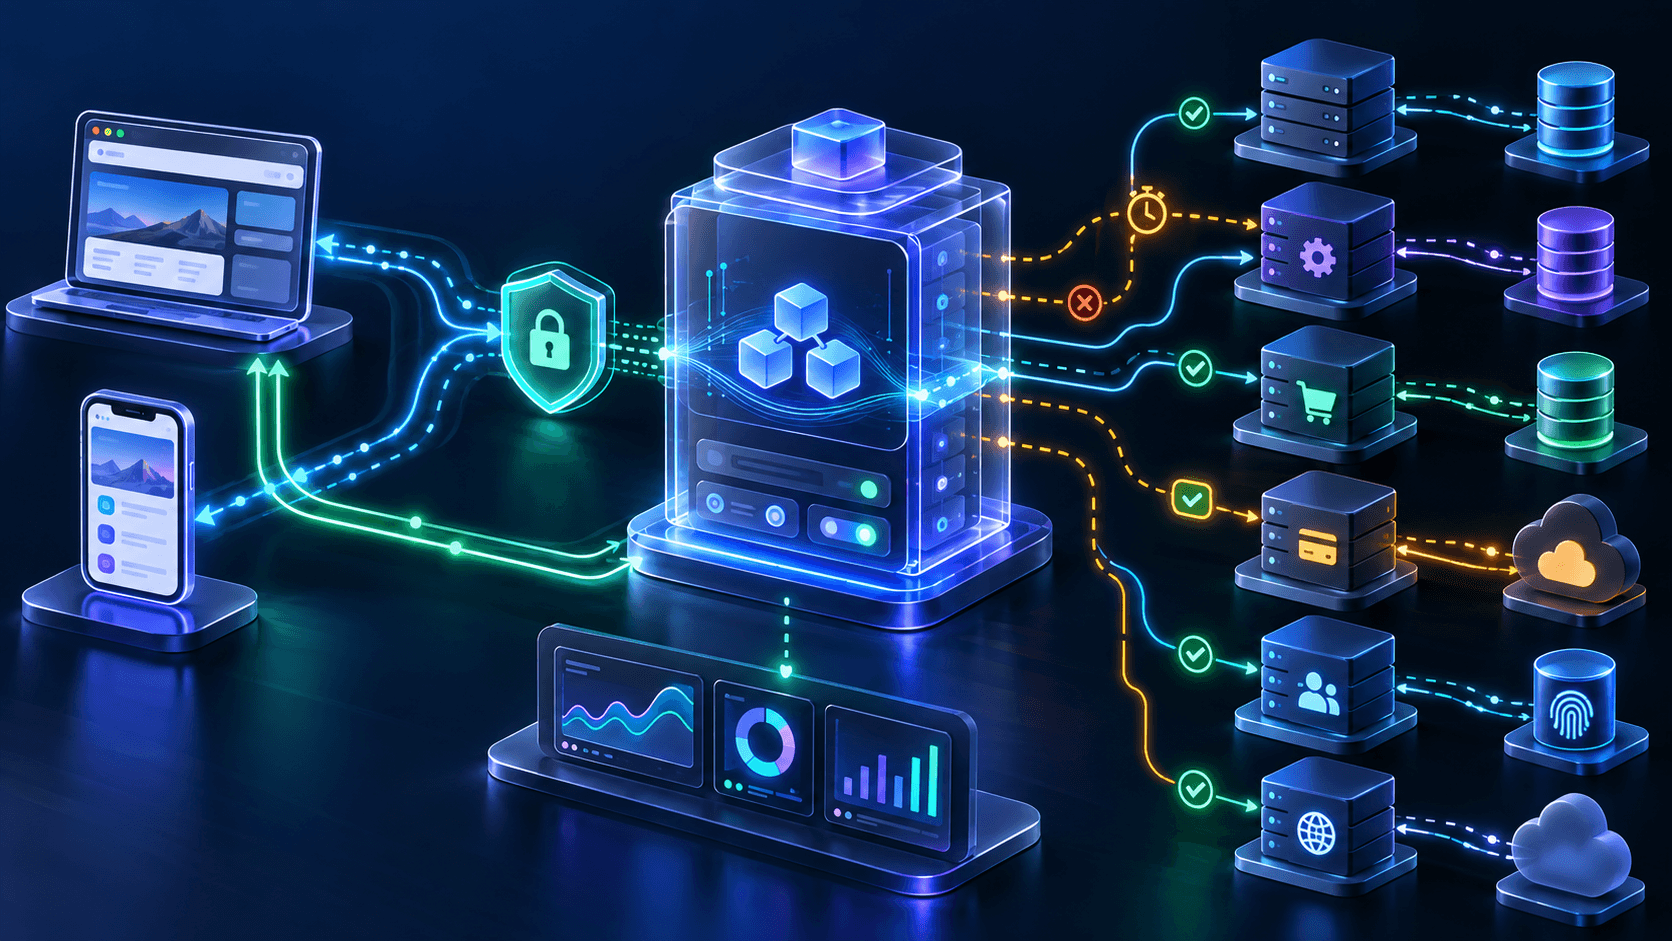
A backend for frontend is a server boundary shaped around one user experience. In a Next.js application it can translate browser-friendly requests into calls to identity, catalog, billing, search, or internal APIs; aggregate their results; and return only the data the page needs.
Good fit
The client needs coordinated data from several services, secure credentials, or a tailored response model.
Poor fit
The layer only forwards every header and payload to one API without adding policy or reducing coupling.
Warning sign
Business rules, system-of-record data, and reusable domain workflows start accumulating inside the UI repository.
Keep durable domain ownership in the services that own the data. Let the BFF own presentation orchestration, client-specific validation, session translation, and response composition.
Give every route a narrow contract and an explicit owner
Organize BFF endpoints by user capability rather than mirroring downstream URLs. A checkout summary route may read prices, inventory, delivery options, and account benefits, but its contract should describe the stable view the client consumes—not expose each provider's raw response.
- Define methods, schemas, status codes, cache behavior, and safe error codes.
- Validate path, query, body, and content type before calling dependencies.
- Return the minimum fields needed for the interface.
- Version intentional breaking changes instead of leaking downstream churn.
- Name the team responsible for availability and contract evolution.
The production controls in our Next.js route-handler guide apply directly to these browser-facing endpoints.
Translate identity once, then authorize every resource
The BFF can exchange a secure session cookie for an internal service credential, but it must not convert authentication into blanket authorization. Resolve the user and tenant on the server, verify the action against the requested resource, and send downstream services a scoped identity that they can independently evaluate.
Keep service credentials out of client bundles and browser-visible responses. Use short-lived tokens, explicit audiences, and least-privilege scopes. For mutations, apply CSRF-aware design, origin checks where appropriate, idempotency, and recent authentication for sensitive actions.
Parallelize independent calls and preserve a single time budget
A BFF that calls five services sequentially turns modest latency into a slow page. Start independent reads together, but limit concurrency and propagate one request deadline so downstream work does not outlive the user request.
const deadline = Date.now() + 1800;
const [account, orders] = await Promise.all([
  getAccount({ signal, deadline }),
  listRecentOrders({ signal, deadline }),
]);

return shapeDashboard({ account, orders });
Use separate connection and response timeouts within the total budget. Cancel outstanding work when the client disconnects. Keep expensive or nonessential enrichment out of the critical path; enqueue durable work after a committed mutation when the result is not required immediately.
Define partial failure before dependencies fail
Aggregation creates choices: should one missing recommendation fail the entire product page, or should the page render without it? Classify every dependency as required, optional, or deferrable and define the user-visible fallback for each.
- Fail closed when identity, authorization, price, or payment state is uncertain.
- Omit or mark stale noncritical content only when the interface can explain it honestly.
- Retry safe transient reads within the deadline, with jitter and a small attempt limit.
- Do not automatically retry ambiguous mutations without an idempotency key.
- Use circuit breaking and bounded concurrency to protect degraded services.
Our circuit-breaker guide covers state, fallbacks, and recovery without masking dependency incidents.
Cache the composed response only when its audience is clear
Public reference data can use shared caches, while personalized responses need private or user-scoped caching. Include every representation-changing input—tenant, role, locale, currency, feature cohort, and authorization state—in the cache design. When that is difficult to prove, prefer no shared cache.
Keep freshness aligned with business risk. A short-lived product description and a payment balance have very different tolerance for staleness. Never cache authorization denials so broadly that a permission change remains invisible, and do not let one tenant's result populate another tenant's response.
Treat the BFF as an internet-facing policy enforcement point
Set payload limits before parsing, allow only expected methods and content types, normalize input once, and encode output for its destination. Do not offer arbitrary upstream URLs, headers, fields, or query fragments; that turns orchestration into an SSRF, injection, or data-exfiltration surface.
Rate-limit by verified account or API identity when possible, add stricter controls to costly fan-out routes, and cap total downstream work per request. Redact cookies, tokens, authorization headers, personal data, and full provider payloads from logs. Apply the supply-chain practices in our Next.js dependency-security guide to every provider SDK the layer imports.
Trace the complete fan-out, not just the outer route
Attach a request ID and trace context to every downstream call. Record route, dependency, attempt, timeout budget, cache outcome, response class, and safe error code. Measure end-to-end latency alongside each dependency's latency so the orchestration overhead remains visible.
Track fan-out count, payload size, partial-response rate, cancellation, timeout, retry, saturation, and error budgets by route and client experience. A healthy outer status code can hide a missing optional service on every request, so emit an explicit degraded-result signal.
Test contracts, failure combinations, and deployment compatibility
Unit-test response shaping and authorization decisions; contract-test each downstream client against supported provider behavior; integration-test timeouts, invalid payloads, stale caches, and credential failures; then run end-to-end tests for the critical user journey.
Deploy contract changes in a backward-compatible sequence. Add new fields before requiring them, support old and new provider versions during migration, and use a measured rollout with dashboards and rollback. Avoid rebuilding a preview or production artifact with different configuration after tests pass.
Next.js BFF production checklist
✓ Routes model client capabilities instead of proxying services blindly
✓ Server identity and resource authorization are enforced separately
✓ Independent calls run in parallel under one deadline
✓ Required and optional dependencies have explicit failure behavior
✓ Cache keys preserve tenant, user, locale, and permission boundaries
✓ Inputs, payload sizes, fan-out, and concurrency are bounded
✓ Traces expose every downstream call and degraded response
✓ Domain rules remain owned by the systems of record
Build a more dependable Next.js application
Endurance Softwares helps teams design, build, test, and operate production-ready Next.js platforms.