


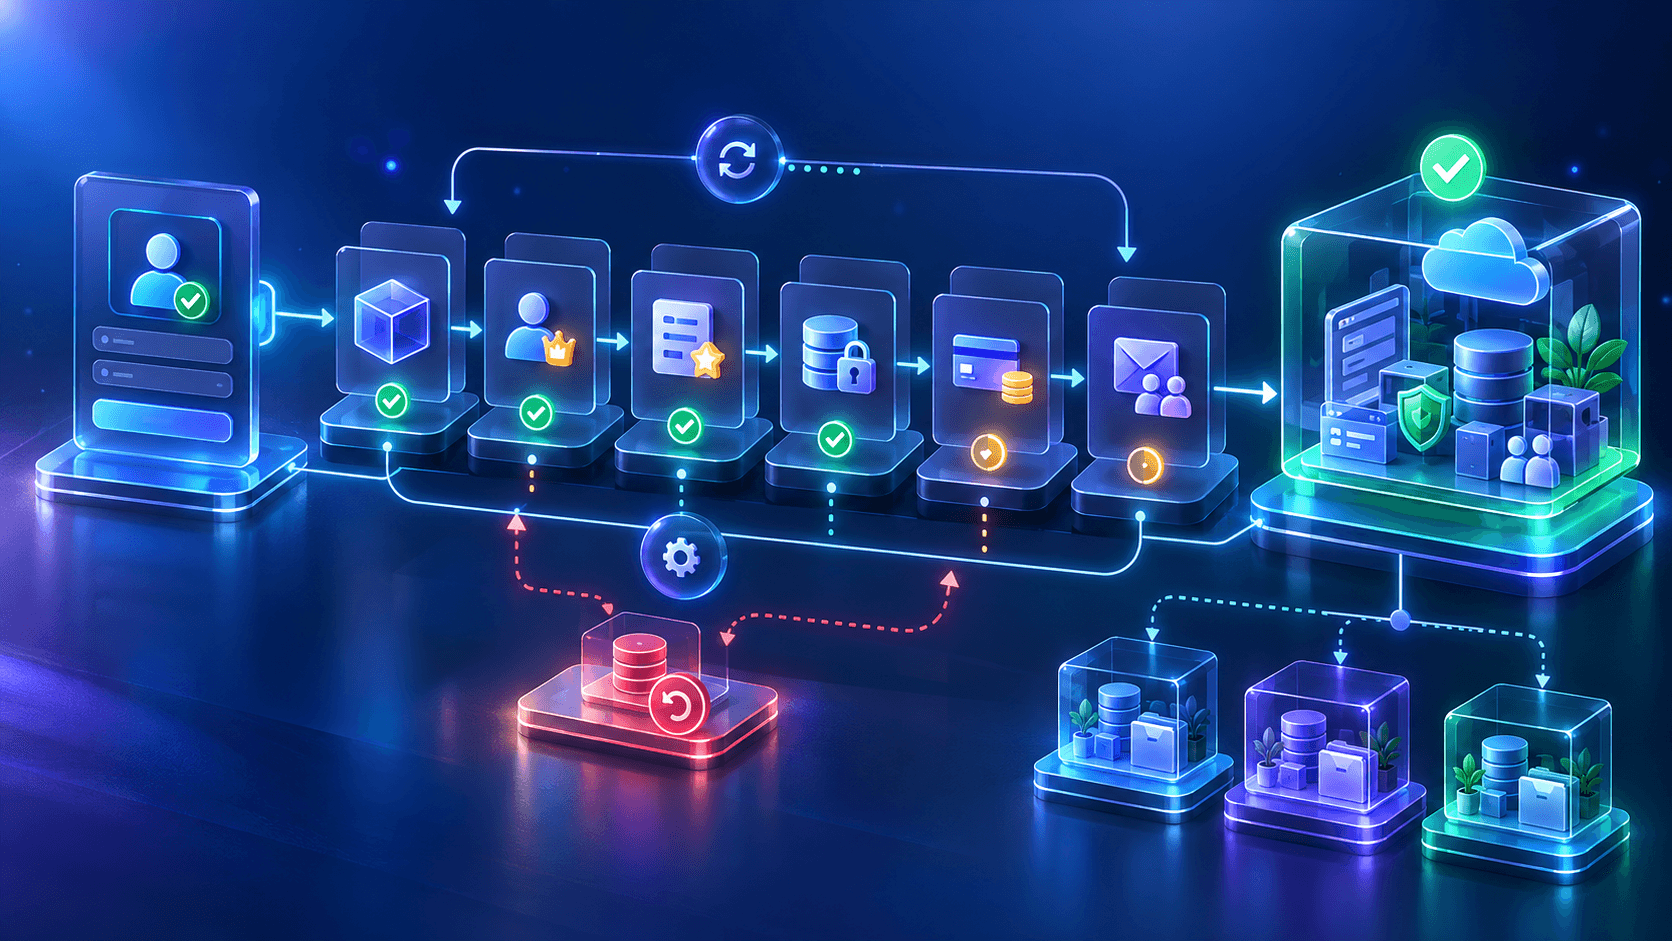
Treat onboarding as a durable workflow, not a long signup request
A production SaaS signup may create an organization, assign an owner, reserve a slug, initialize settings, apply plan entitlements, start billing, seed data, configure integrations, and send invitations. Performing every step inside one Next.js request makes a network timeout indistinguishable from failure and leaves partially created tenants difficult to repair.
Accept
Validate the request, verify identity, reserve uniqueness, and create one provisioning record.
Provision
Run idempotent steps asynchronously with explicit dependencies, attempts, and outcomes.
Activate
Expose the workspace only after its required security and product invariants are true.
Return a stable operation ID and status URL. The interface can show meaningful progress while workers continue independently of the browser connection.
Make every transition explicit and recoverable
Store the desired plan, region, tenant owner, policy version, current state, step results, retry schedule, and safe failure reason. Use a constrained state machine instead of several unrelated booleans that can contradict each other.
requested → identity_verified → tenant_created
          → owner_assigned → resources_ready
          → billing_ready → active

any step → retrying | needs_review | compensating
Transition state atomically and publish follow-up work through a durable outbox or queue. The transactional outbox pattern closes the gap between a committed database change and the job that advances it.
Make repeated signups and worker retries converge
Browsers retry, payment providers resend events, and workers can crash after completing a side effect. Accept an idempotency key for the signup intent, enforce database uniqueness for tenant slugs and memberships, and give each provisioning step a stable operation key.
- Claim steps atomically so two workers cannot initialize the same resource.
- Record external resource IDs before acknowledging work.
- Query uncertain provider state before repeating an ambiguous call.
- Retry transient failures with backoff and jitter; stop on permanent validation failures.
- Move exhausted workflows to a reviewable state rather than silently abandoning them.
Establish tenant boundaries before writing tenant data
Create the tenant identifier first and require it at every repository, cache, queue, storage, search, and analytics boundary. Do not let a partially provisioned user choose an arbitrary tenant ID in later requests. Resolve tenant context from trusted membership and server-side routing.
Assign the initial owner membership in the same transaction as the tenant whenever possible. Default-deny other access until roles and policies are ready. Our PostgreSQL row-level security guide explains how database policy can reinforce application checks.
Snapshot the purchased offer into versioned entitlements
A marketing plan name is not an authorization policy. Translate the selected offer into a versioned set of limits and capabilities—seats, storage, projects, integrations, retention, and support level—and store the result with its effective date.
Provisioning should use this snapshot rather than rereading mutable pricing content at each step. When billing changes later, process a separate, auditable entitlement transition. Keep feature rollout flags distinct from commercial entitlements: one controls release exposure, while the other expresses what the customer purchased.
Separate workspace creation from payment confirmation
Create provider customers and subscriptions with stable idempotency keys, then treat signed provider webhooks as authoritative for asynchronous payment state. A browser redirect can improve the experience but must not activate paid capabilities by itself.
- Store provider IDs against the tenant, not only the initiating user.
- Verify webhook signatures and deduplicate provider event IDs.
- Handle trial, incomplete, active, past-due, canceled, and disputed states explicitly.
- Make compensation policy clear before charging: retry, void, refund, or require support review.
Issue invitations only after the workspace can enforce them
Generate random, single-purpose invitation tokens, store only a protected representation, set an expiry, and bind each invitation to tenant, email or identity rule, role, and inviter. Accepting an invitation must recheck that the tenant is active, the role still exists, and the recipient is eligible.
Sending an email is a separate durable step. Use the queue, retry, webhook, and suppression practices in our Next.js transactional email guide. A delayed invitation must not block core tenant activation.
Show truthful progress and preserve resumability
Map technical states to a small set of understandable UI states: setting up, ready, action required, or delayed. Poll with a bounded interval or use a trusted event channel, and let the user safely resume after closing the tab. Never display raw provider errors, secrets, or internal topology.
Keep product onboarding tasks—profile completion, first project, teammate invitation—separate from infrastructure readiness. The workspace can be technically active while guided setup remains incomplete. Measure both time-to-ready and time-to-first-value.
Observe each step and reconcile unfinished tenants
Trace the signup request through tenant creation, jobs, provider calls, webhooks, and activation. Track workflow age, per-step latency, retry counts, duplicate suppression, compensation, abandoned signup, and activation conversion. Exclude tokens, payment details, and unnecessary personal data from logs.
Run a scheduled reconciler that finds workflows stuck beyond their expected deadline, compares internal and provider state, and either safely resumes or raises a support task. Test worker crashes, duplicate requests, provider timeouts, webhook reordering, plan changes mid-flow, and deletion during provisioning.
Next.js SaaS provisioning checklist
✓ Signup returns a durable operation instead of holding one long request
✓ Workflow transitions and required activation invariants are explicit
✓ Repeated requests and workers converge through idempotency
✓ Tenant identity scopes every data and infrastructure boundary
✓ Versioned entitlements represent the purchased offer
✓ Signed billing webhooks—not redirects—control payment state
✓ Invitations are expiring, single-purpose, and re-authorized
✓ A reconciler detects and repairs stuck provisioning workflows
Build a more dependable Next.js application
Endurance Softwares helps teams design, build, test, and operate production-ready Next.js platforms.