


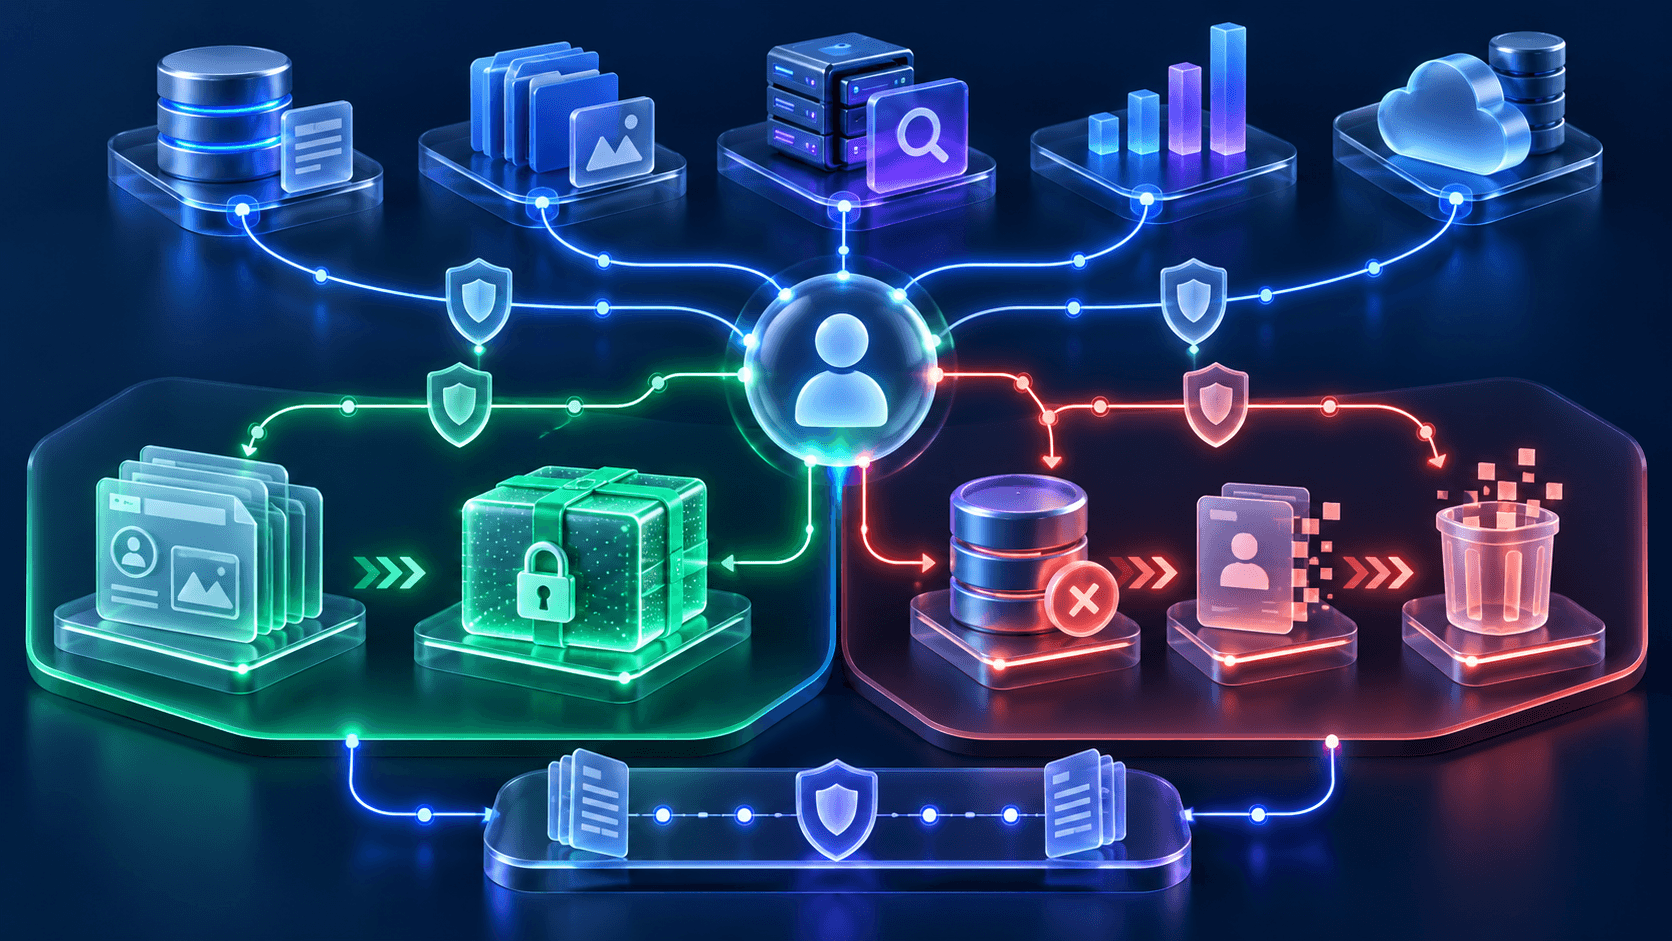
Start with a map of user data, not a delete button
A Next.js account rarely lives in one row. Profile data may appear in relational tables, object storage, search indexes, analytics, support tools, authentication providers, queues, caches, logs, and vendor systems. An export or deletion flow is only as complete as this inventory.
Source
Name the system of record, owner, identifier, data class, and tenant boundary.
Purpose
Document why the data exists, how long it is useful, and which product workflow depends on it.
Disposition
Choose export, deletion, anonymization, retention, or exclusion with an accountable policy owner.
Represent this as a maintained registry consumed by the workflow rather than a checklist hidden in a ticket. Product, security, and legal stakeholders should approve policy; engineering should make execution explicit, testable, and observable.
Model privacy requests as durable state machines
Large exports and multi-system deletions should not run inside one browser request. Create a request record with an opaque ID, tenant, subject, policy version, requested action, status, timestamps, and step results. Then enqueue bounded jobs and expose a safe status endpoint.
requested → identity_verified → approved → processing
          → completed
          → partially_failed → retrying
          → rejected_or_cancelled
Transitions should be atomic and idempotent. Store stable operation keys so a retried worker cannot create multiple archives or repeat an irreversible vendor action. Use the reliability patterns in our Next.js background-work guide for leases, retries, and recovery.
Verify the person and the scope before collecting data
An authenticated session is a useful signal, not always sufficient proof for a sensitive export or destructive action. Require recent authentication, step-up verification for higher-risk accounts, and a confirmation that names the affected workspace, account, or organization.
- Resolve the subject from trusted server-side identity, never a submitted user ID alone.
- Apply tenant and resource-level authorization to every collector.
- Require an appropriate organization role before exporting shared business data.
- Invalidate the flow when credentials, membership, or account ownership change.
- Protect initiation and confirmation endpoints against CSRF and automated abuse.
Support-assisted requests need a separate, reviewed path with dual control for sensitive cases. Record who authorized the operation without copying secrets or identity evidence into ordinary logs.
Build exports from versioned collectors and deliver them briefly
Each data source should implement a versioned collector with explicit fields, pagination, tenant filters, and error behavior. Prefer portable formats such as JSON and CSV, document timestamps and units, and include a manifest explaining the archive structure and generation time.
Stream large results into encrypted object storage instead of buffering them in a serverless function. Use a random object key, a short retention window, server-side encryption, and a single-purpose download route that rechecks authorization before issuing a short-lived signed URL. Do not attach sensitive exports to email.
Separate access removal, deletion, and anonymization
Immediately revoke sessions, API keys, scheduled actions, and account access when a confirmed deletion begins. That containment step is different from removing every retained record, which may take longer and may be constrained by legitimate policy decisions.
Define dependency order so child records, files, indexes, caches, and derived aggregates do not recreate deleted data. Hard-delete records that no longer have a purpose; irreversibly anonymize records that must preserve aggregate or referential integrity; and retain narrowly required records under a documented policy with access restrictions.
- Replace personal identifiers with non-reversible values, not merely null display fields.
- Remove file originals, thumbnails, transformations, and CDN references.
- Delete search documents and prevent change-data pipelines from reindexing them.
- Tombstone queued jobs and events so stale consumers cannot restore the profile.
- Send vendor deletions with stable request IDs and record their acknowledged outcome.
Make retention executable across primary systems and backups
A retention policy that exists only in prose will drift. Schedule deletion or anonymization by data class, verify the affected counts, and alert when records exceed their deadline. Legal holds or contractual retention exceptions should be narrow, authorized, time-bounded, and visible to the workflow.
Immutable backups usually cannot be edited safely record by record. Instead, limit backup lifetime, encrypt them, tightly restrict restore access, and keep a deletion ledger that is reapplied if an older backup is restored. Test this process: a restore is incomplete until previously completed deletions are enforced again.
Prove the workflow without rebuilding the deleted profile
Record request state transitions, policy version, actor type, system steps, counts, safe reason codes, and completion evidence. Avoid storing exported fields, raw archive paths, verification secrets, or detailed personal content in the audit trail.
Use pseudonymous request and subject references with tightly controlled lookup. Set a separate retention policy for operational evidence. Our Next.js audit logging guide covers server-side identity, tamper resistance, scoped search, and pipeline health.
Test policy changes and failure recovery as production features
Use synthetic accounts containing every supported data type, then verify the export manifest and query each destination after deletion. Interrupt workers between steps, replay duplicate events, expire signed links, rotate credentials, simulate vendor outages, and restore a backup containing a deleted subject.
Track request age, time in each state, failed steps, retry counts, archive size, expired downloads, retained exceptions, and overdue vendor confirmations. Alert before the promised service window is exhausted. Review the data inventory whenever a team adds a table, event, analytics property, upload, or external processor.
Next.js privacy workflow checklist
✓ A maintained registry maps every relevant data destination
✓ Recent identity verification and tenant authorization guard requests
✓ Export and deletion run as durable, idempotent workflows
✓ Archives are encrypted, short-lived, and authorization-checked
✓ Deletion prevents queues and indexes from recreating data
✓ Retention exceptions have owners, reasons, and expiry
✓ Backup restores reapply completed deletion records
✓ Audit evidence excludes the sensitive data being removed
Build a more dependable Next.js application
Endurance Softwares helps teams design, build, test, and operate production-ready Next.js platforms.